This is not just a tiny chip problem
A toner cartridge looks like a consumable, but the authentication chip protects revenue, warranty exposure, print quality, and channel trust.
The story moves from attacker incentives to PKI authentication, then to the central failure point: if the private key can be read or copied, the whole proof collapses.
PUF and Secure Storage solve different parts of the problem. PUF makes the chip identity hard to clone; Secure Storage keeps counters, certificates, and state from being rolled back or forged.
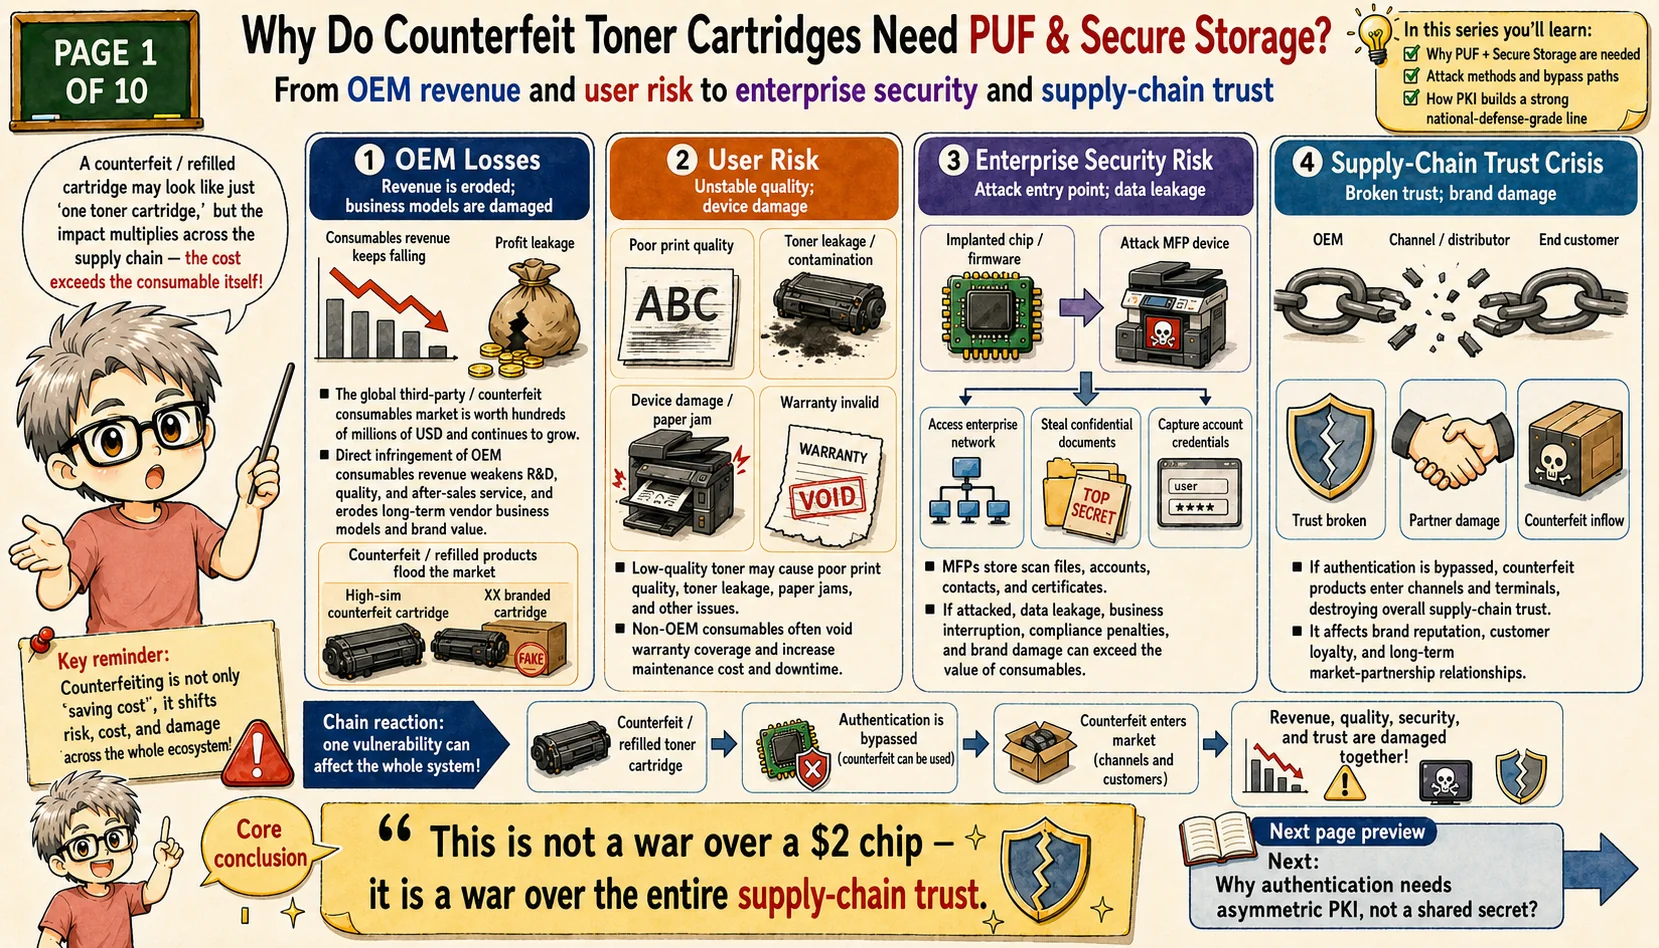
A toner cartridge is a business asset, not just a consumable
The first page explains the economic reason behind the security story. In many printer ecosystems, the printer can be sold at a low margin while cartridges create long-term recurring revenue. That makes the cartridge authentication chip a direct target for counterfeiters and unauthorized refill or reuse attacks.
The authentication chip is the small guard inside the cartridge. Its job is to prove to the MFP that the cartridge is genuine. If this proof can be copied, reset, or forged, the attacker does not need to beat the whole printer business. They only need to defeat the trust anchor inside the consumable.
The important teaching point is that cartridge security is not protecting a low-cost chip for its own sake. The chip protects recurring revenue, service quality, warranty exposure, and channel trust. A very small authentication IC can therefore protect a much larger business system.
From an engineering viewpoint, the MFP cannot inspect toner quality or packaging labels in a trustworthy way. It has to rely on cryptographic identity, protected counters, and tamper-resistant state. That is why the lesson starts from business incentive and immediately moves toward hardware trust.
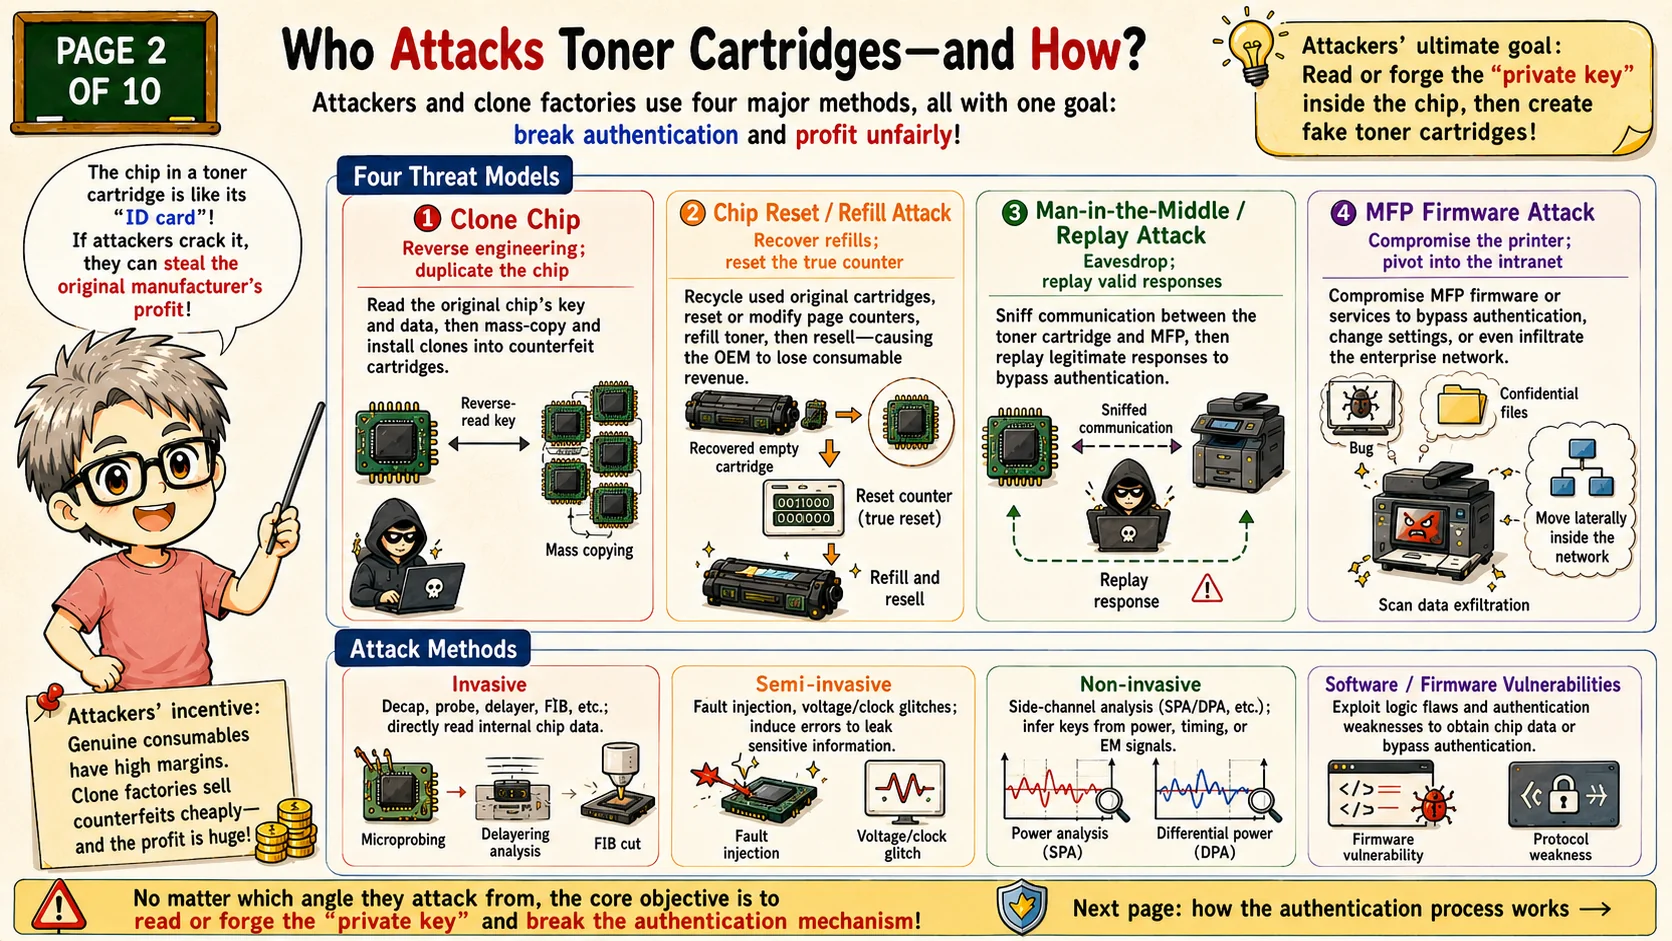
Attackers target authentication because profit is on the other side
The second page separates the main threat models: cloned chips, remanufacturing or counter reset attacks, man-in-the-middle and replay attacks, and attacks against the MFP firmware itself. Each path tries to make a non-genuine or reused cartridge look acceptable to the printer.
The attack methods span physical probing, decapsulation, FIB work, fault injection, side-channel analysis, protocol weaknesses, and firmware vulnerabilities. Different attackers use different tools, but the security objective is the same: bypass authentication and recover the economics of a genuine cartridge without being genuine.
The diagram also separates goals from techniques. Cloning tries to copy identity. Remanufacturing tries to reset lifecycle state. Replay tries to reuse a past valid conversation. Firmware compromise tries to move the attack boundary into the printer. A complete design has to consider all of them.
This is why protocol security alone is not enough. A perfect challenge-response protocol still fails if the private key is stored in readable memory. A protected private key still leaves risk if counters and state flags can be rolled back. The defense must combine authentication, key protection, and secure state storage.
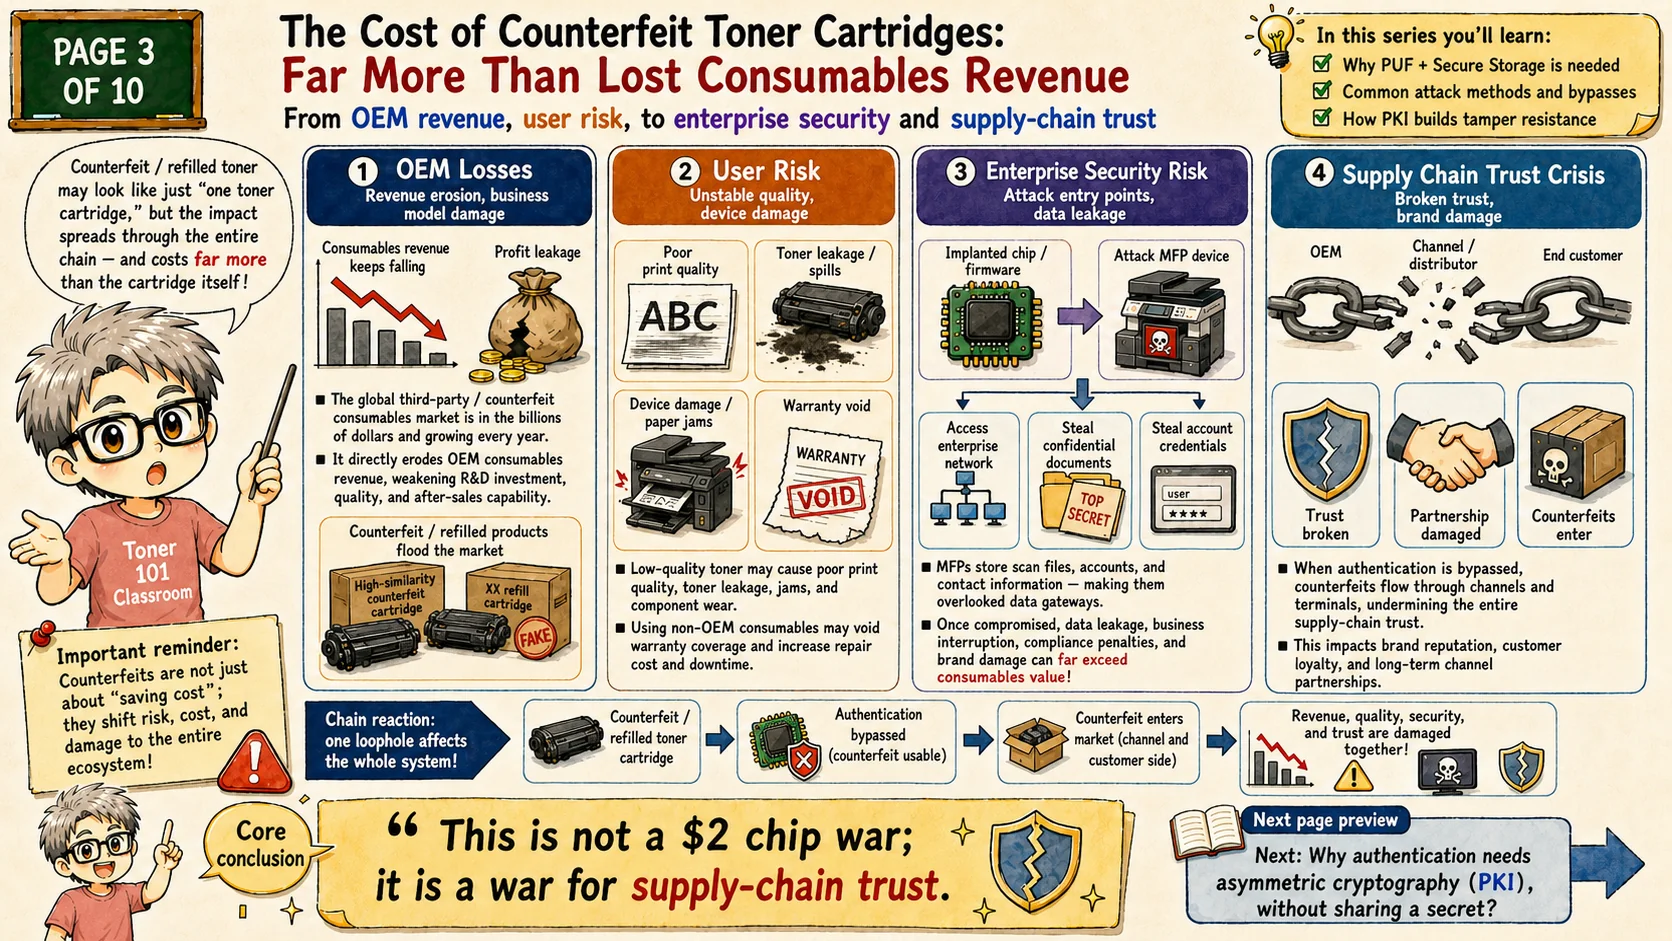
The loss is larger than consumable revenue
Counterfeit cartridges hurt OEM consumable revenue, but the damage does not stop there. Users may get poor print quality, toner leakage, machine damage, extra service cost, and warranty disputes. Distributors and partners also lose trust when fake or reset supplies move through the channel.
In enterprise environments, the MFP is also a networked device that touches scanned documents, credentials, and internal workflows. A compromised cartridge interface or authentication path can therefore become part of the broader printer security attack surface.
The four boxes in the page show how risk propagates. Revenue loss is the visible layer, but service cost, user dissatisfaction, warranty handling, brand damage, and channel disputes can be just as important. Security failure becomes an operational problem.
For enterprise buyers, the printer is not a harmless peripheral. It is a networked endpoint with memory, firmware, credentials, scanned documents, and administrative settings. Consumable authentication should therefore be treated as part of the device security boundary.
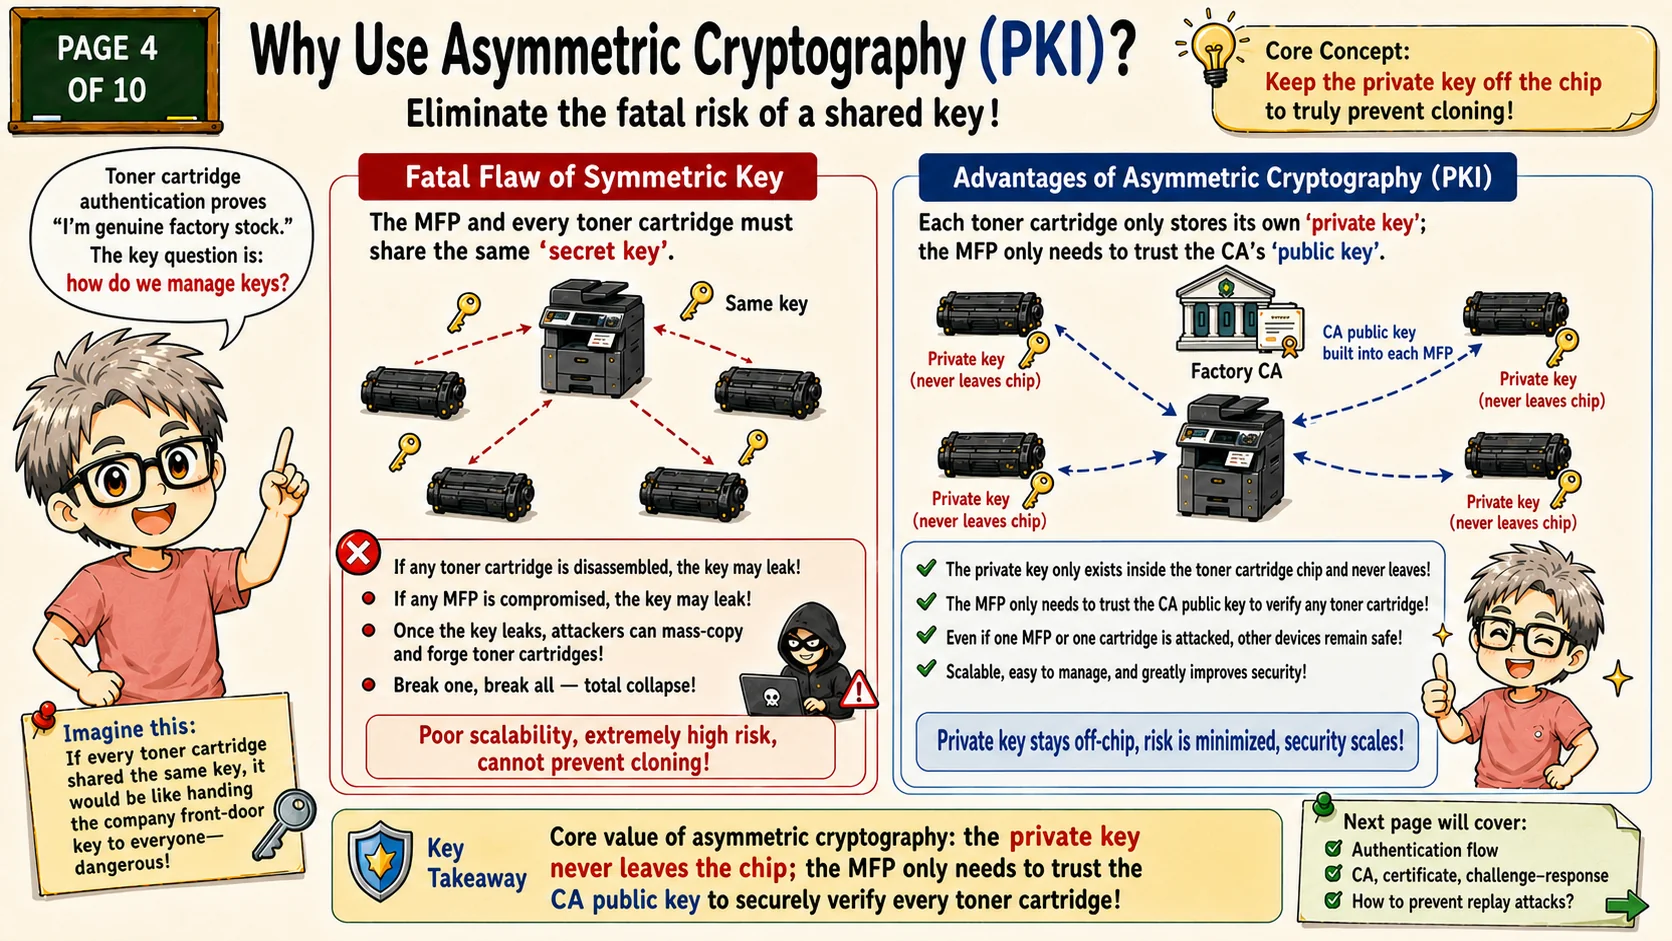
PKI avoids the break-one-break-all problem
A shared symmetric secret is dangerous in this setting. If the same secret is reused across cartridges or devices, extracting it from one place can compromise the whole ecosystem. That is the classic break-one-break-all failure mode.
With asymmetric authentication, each cartridge proves possession of its own private key. The MFP only needs the OEM CA public key to verify device certificates and signatures. This improves scalability and containment: one compromised endpoint should not automatically reveal the secret for every other cartridge.
PKI separates verification power from impersonation power. The MFP can verify a certificate and signature, but it cannot produce a cartridge signature by itself. That separation is what makes large fleets manageable: the verifier can be widely deployed without becoming the universal secret.
However, PKI only shifts the problem to private-key protection. If the private key is injected insecurely, stored in plain NVM, exposed through test mode, or leaked through debug access, the asymmetric design loses its main advantage. The private key must be protected by hardware design, not by policy alone.
Challenge-response proves possession of the private key
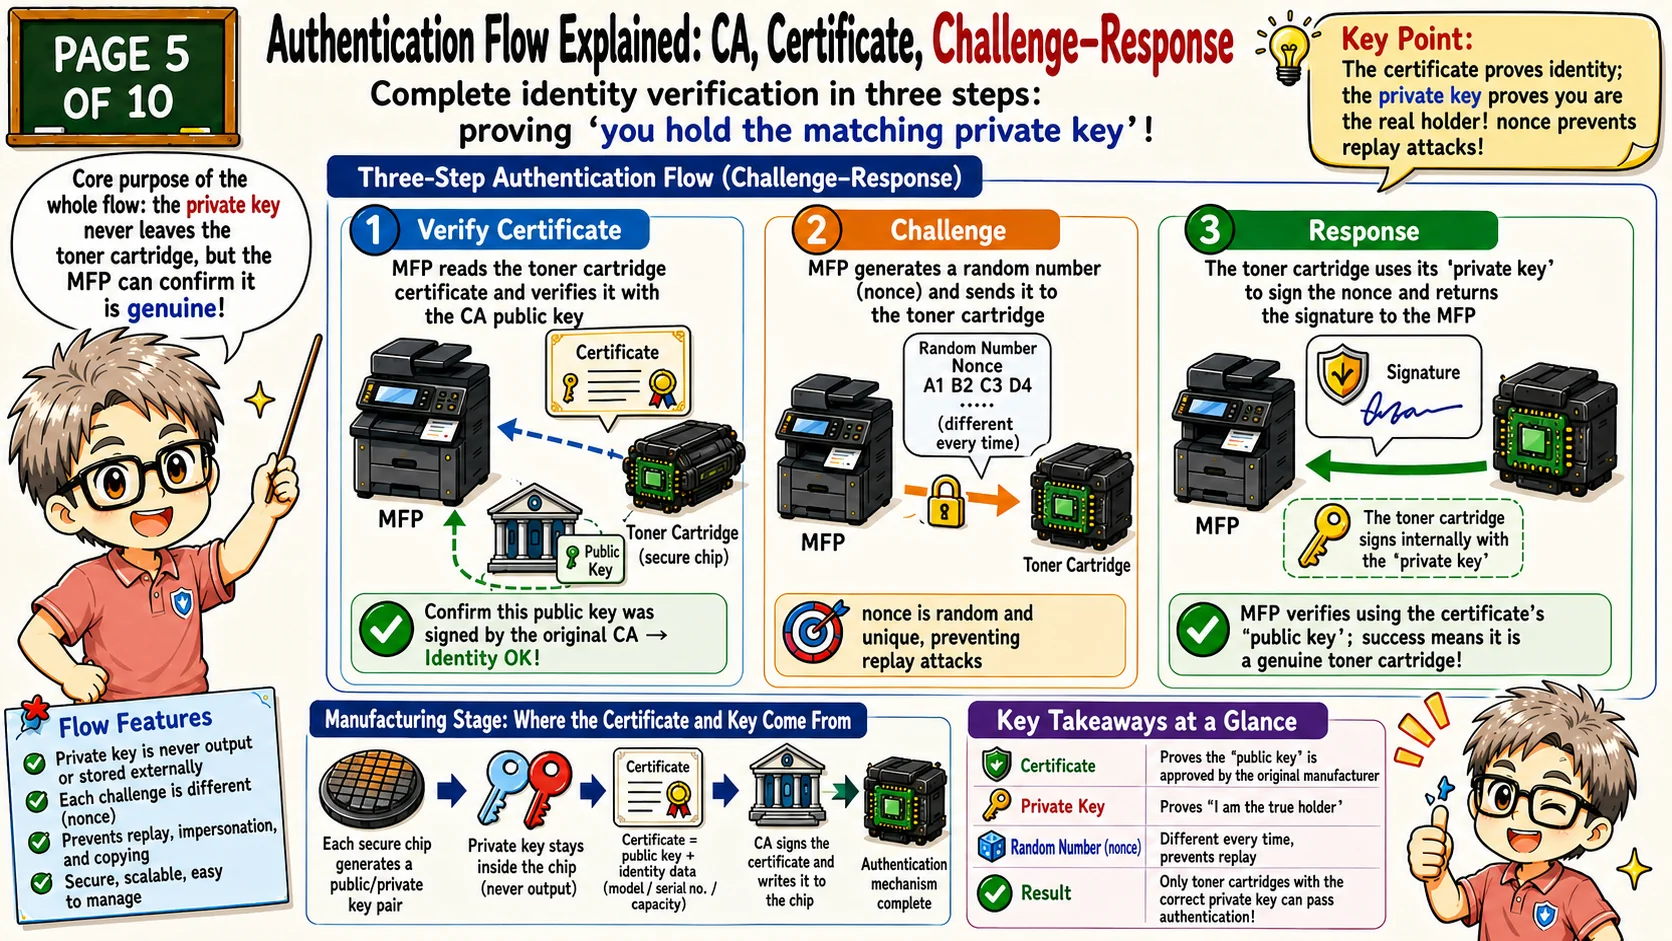
The authentication flow has three practical steps. First, the MFP reads the cartridge certificate and verifies that it was signed by the OEM CA. Second, the MFP sends a fresh random nonce. Third, the cartridge signs that nonce with its private key, and the MFP verifies the signature with the certified public key.
A verifier must generate an unpredictable fresh nonce, bind it to the session, purpose and devices, and reject consumed challenges. A verified signature then supports possession of the matching private key. Certificate path, trust anchor, model and lifecycle policy remain separate checks. A nonce field alone does not establish replay or relay resistance.
Each step answers a different question. The certificate answers: is this public key recognized by the OEM? The nonce answers: is this session fresh? The signature answers: does this cartridge currently possess the matching private key?
The flow is also intentionally auditable. The MFP does not need to know every cartridge's secret. It only needs the CA public key, certificate parsing rules, nonce generation, and signature verification. This is how cryptographic identity becomes practical in a low-cost consumable ecosystem.
From the attacker's view, both the key and verification path matter
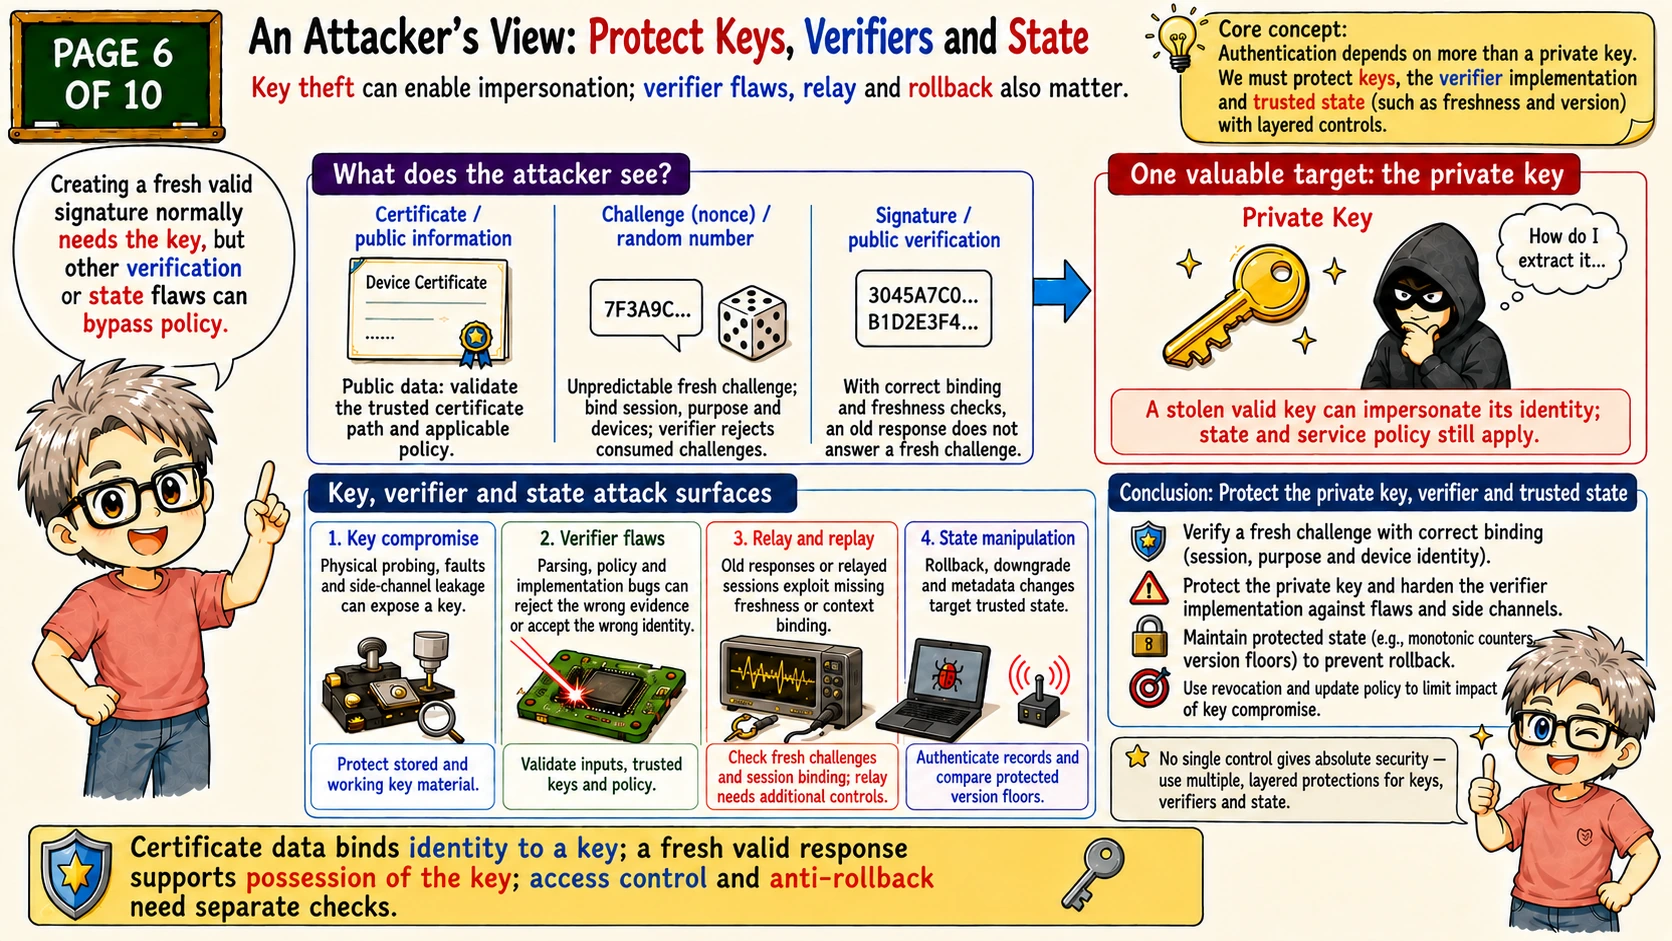
Certificates are public information and cannot alone create a new signature. Correct challenge validation prevents old responses from answering a fresh request. The private key is therefore a valuable target, but not the only one: a verifier flaw, relay or state rollback may avoid extracting it.
If the private key is extracted, the attacker can generate valid signatures and impersonate the original cartridge. This is why the private key needs hardware-root-of-trust level protection, not just ordinary storage in readable non-volatile memory.
The attacker may try several paths to reach that key: read NVM or eFuse contents, probe internal buses, induce faults during signature operations, measure power or electromagnetic leakage, or compromise firmware paths that handle sensitive data.
A strong chip therefore needs more than an algorithm block. It needs locked debug and test modes, controlled key access, side-channel-aware implementation, tamper response, and clear rules for when secrets are generated, used, erased, or denied.
Traditional key storage creates a static target
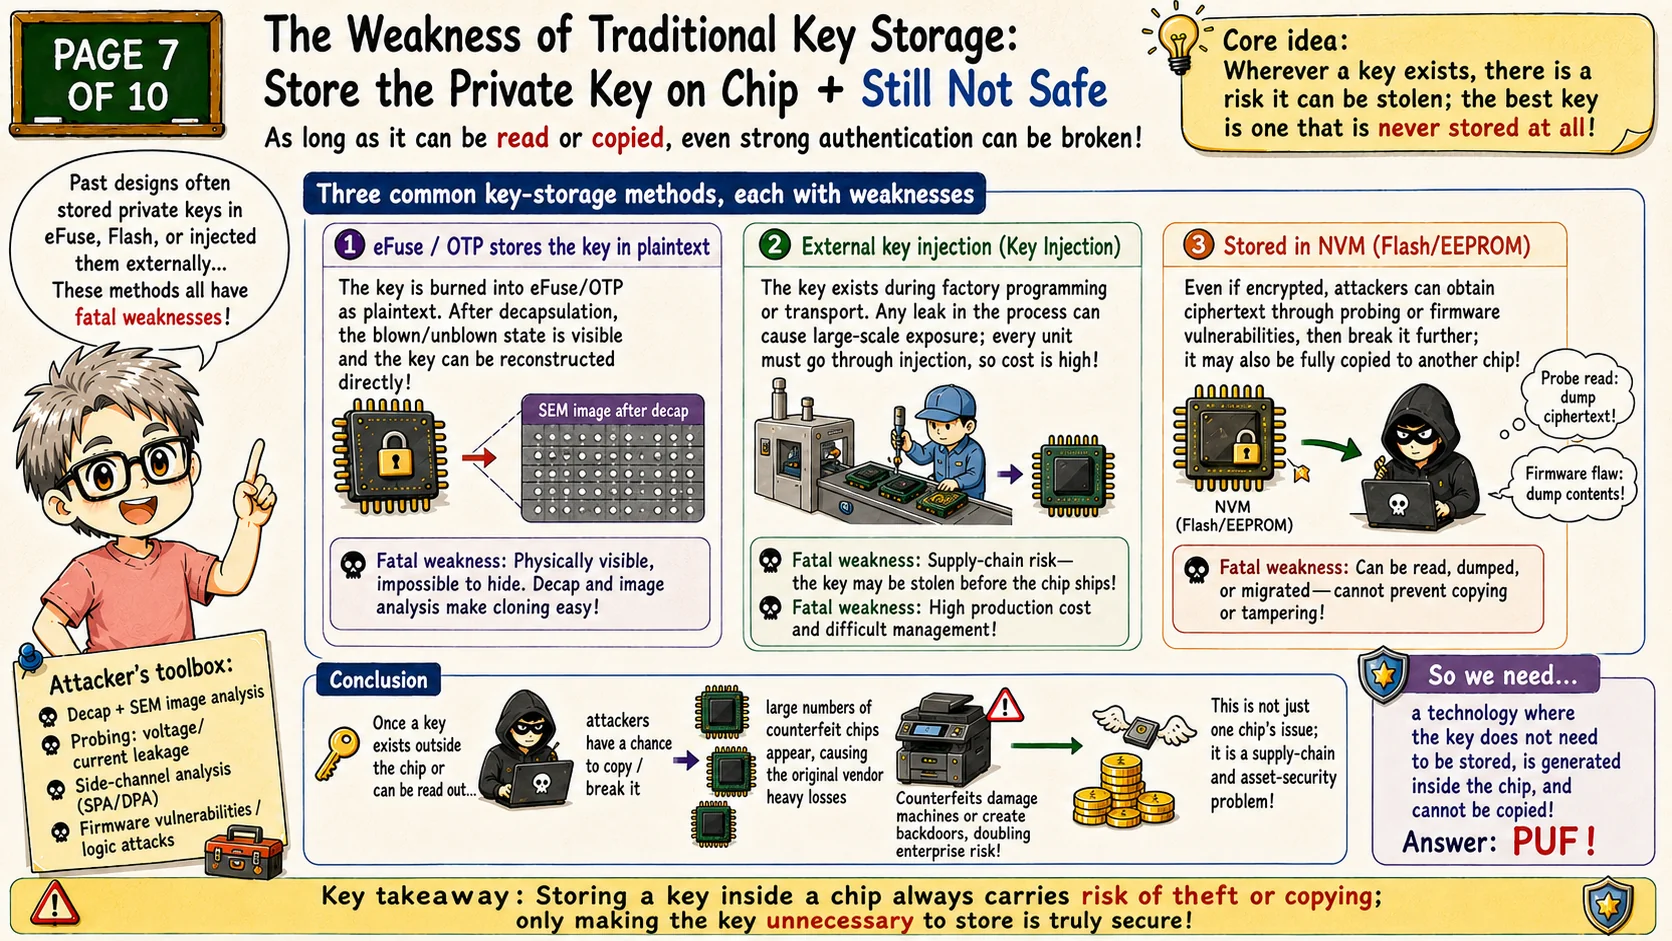
Keys stored in eFuse, OTP, flash, EEPROM, or injected through a factory process can become attack targets. Physical inspection, probing, memory dumps, supply-chain leakage, and migration attacks all become more attractive when the secret exists somewhere at rest.
The teaching point is not that every traditional storage method is always broken. It is that storing a long-term private key creates something an attacker can focus on. Reducing readable secrets at rest can narrow one attack surface. Compare regeneration reliability, temporary key copies, provisioning and side-channel risks; protected conventional storage can also meet a product’s needs.
The page compares three storage weaknesses. Plain eFuse or OTP may be simple, but the programmed state can become physically observable. Factory key injection can work, but it expands the trust boundary to production equipment, databases, logistics, and partners. NVM storage can be encrypted, but then the design must still protect the data-encryption key and anti-rollback state.
This is the bridge to PUF. Instead of asking where to hide the root key, the architecture asks whether the root key can be regenerated from the chip's own physical behavior when needed, then removed from volatile working state when it is no longer needed.
PUF turns silicon variation into a chip fingerprint
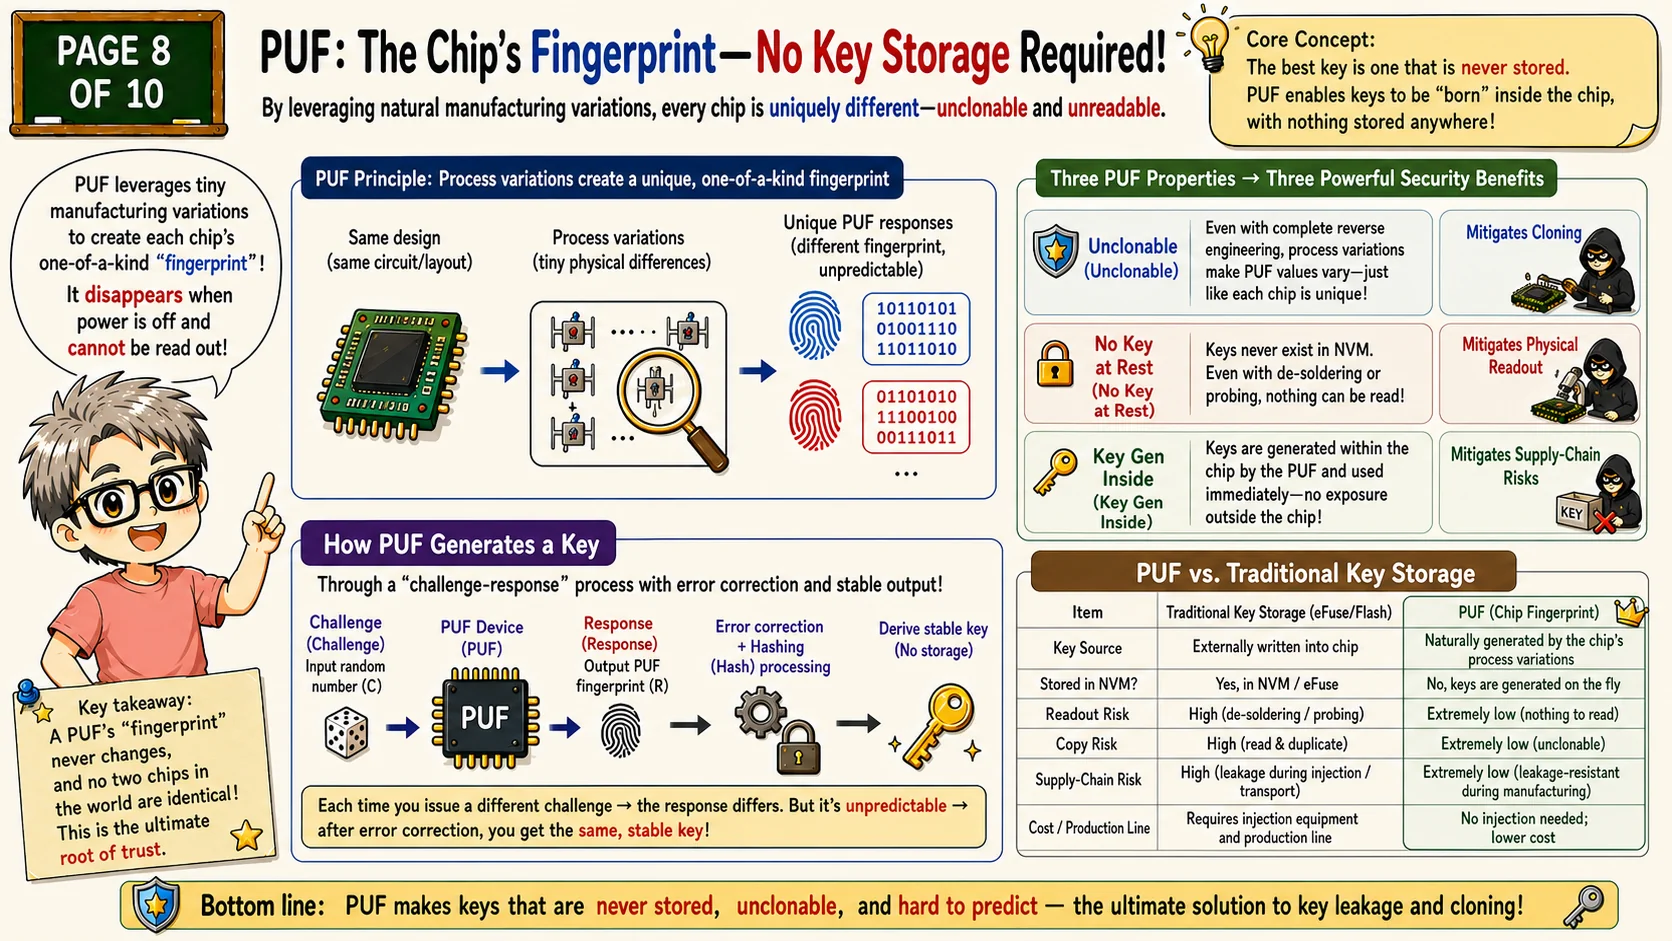
A Physical Unclonable Function uses natural manufacturing variation to produce a chip-unique response. Even if two chips share the same design and process, microscopic differences make their PUF behavior different.
Uniqueness, reproducibility and practical unclonability are properties to measure, not guarantees supplied by the name. Test entropy, noise across temperature and aging, helper-data handling, and resistance to modeling and physical attacks. Regenerating a root key can avoid plaintext NVM storage, but temporary copies, access control, side channels and erasure still need protection.
A production PUF flow usually does not use raw noisy bits directly as a private key. It uses enrollment, helper data, error correction, hashing, and a key derivation function to turn physical behavior into a stable cryptographic secret.
That distinction matters. PUF is not just a slogan meaning 'random chip behavior.' It is a controlled engineering pipeline that turns silicon variation into a dependable identity or root key while keeping the critical secret bound to the original chip.
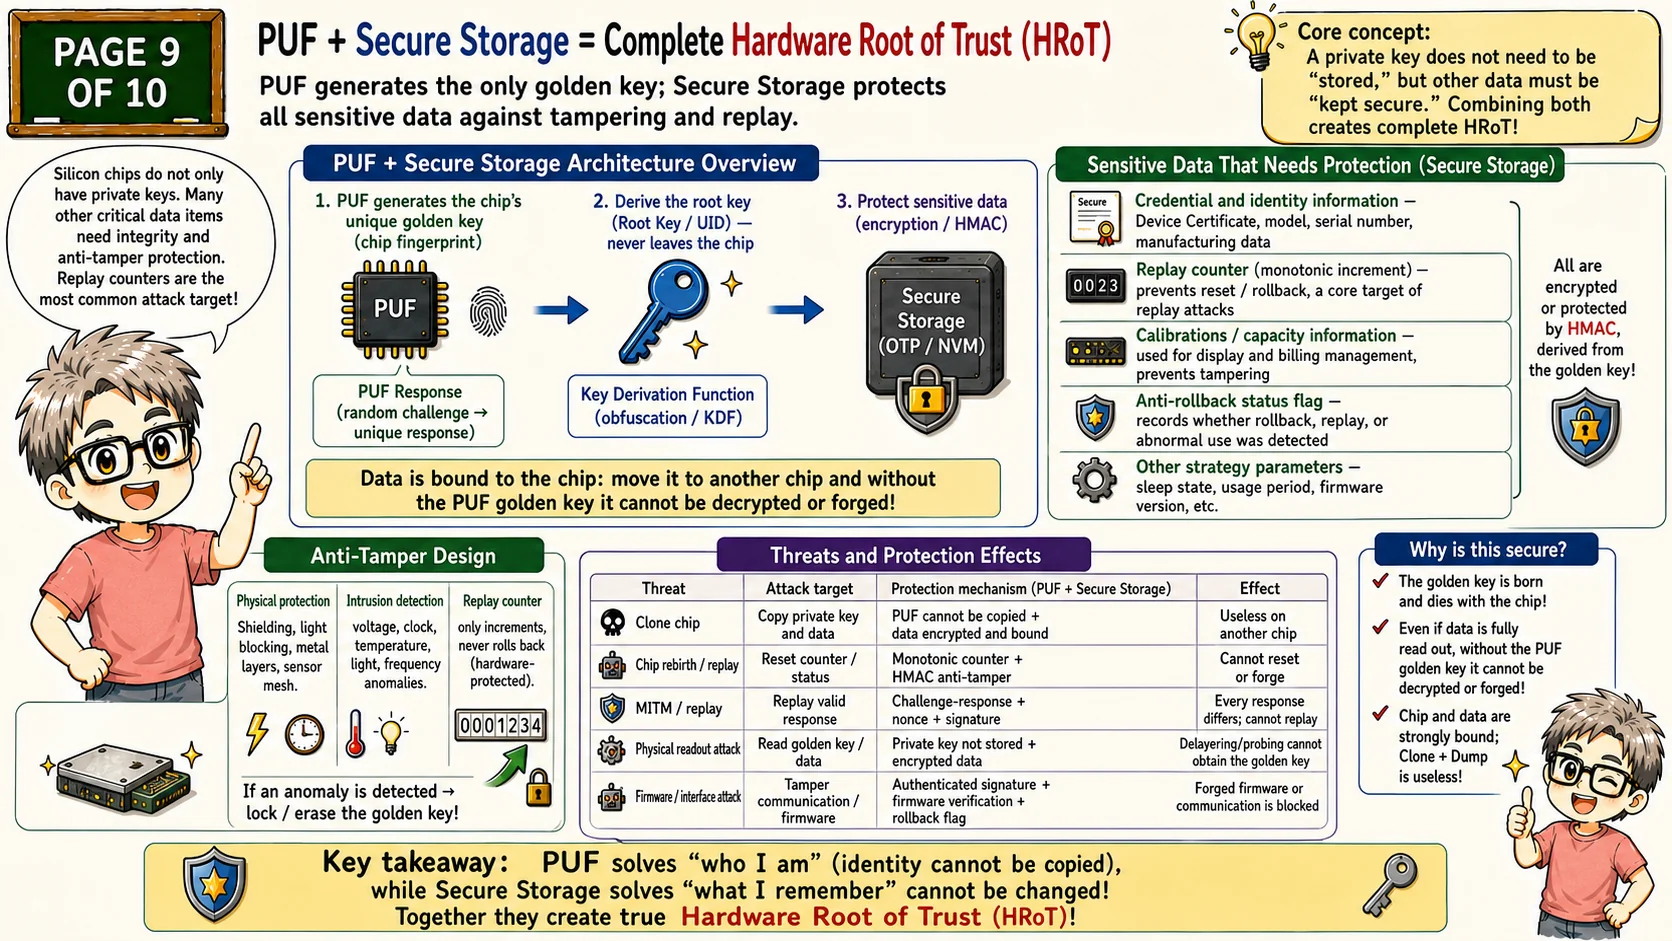
Secure Storage protects the data that must not be changed
PUF solves the identity and root-key problem, but the cartridge also has data that must remain authentic: device certificates, page counters, toner level, anti-remanufacturing state flags, lifecycle status, and version information.
Encryption, HMAC or AEAD can protect content and integrity; device-specific keys can bind records to a chip. Anti-rollback needs an independent protected version or monotonic state. An old record may still decrypt and have a valid tag. The experiment compares counter=10 with a protected floor of 11: authentication passes, but freshness rejects it. Removing floor protection exposes that gap.
Secure Storage therefore needs several properties at once: confidentiality so dumped data is not readable, integrity so modified data is detected, freshness so old data cannot be replayed, and device binding so the protected state cannot simply be copied to another chip.
This is where cartridge security becomes more than identity. A genuine cartridge still needs trustworthy memory for counters and lifecycle flags. Without that, a used cartridge can be reset, downgraded, or rolled back even if the authentication key itself was never extracted.
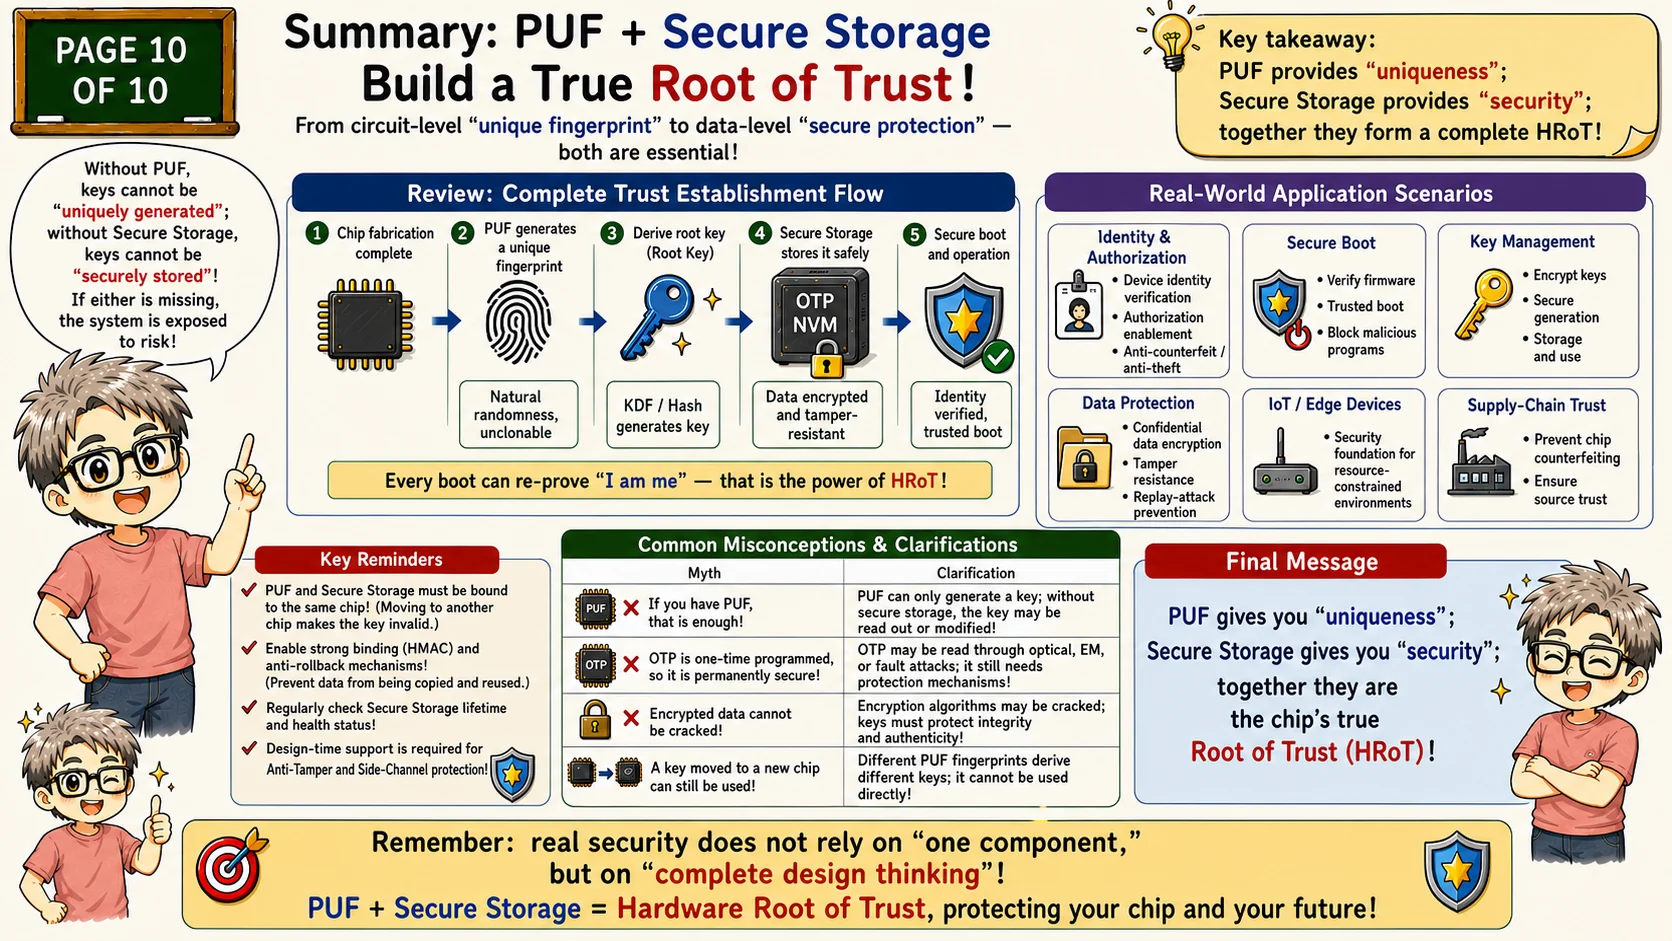
PUF plus Secure Storage creates the real root of trust
The conclusion is architectural. PUF provides chip uniqueness and no-key-at-rest root-key generation. Secure Storage provides integrity, confidentiality, anti-rollback, and anti-tamper support for the records that the system depends on.
Certificates carry a public-key/identity binding that the verifier checks against its trusted path and policy. A valid response to a fresh challenge supports key possession. PUF can support a device-specific secret; Secure Storage protects surrounding state. Anti-cloning, rollback resistance and access limits still require their own evidence.
Read the final page as a trust chain. Silicon variation creates a PUF response. The response derives a root key. The root key protects Secure Storage. Secure Storage preserves certificates, counters, flags, and lifecycle data. PKI and challenge-response expose that protected identity to the MFP.
The practical takeaway is that no single primitive solves the whole problem. PUF answers 'is this the original chip?' Secure Storage answers 'has the protected state remained authentic?' Challenge-response answers 'is this session fresh and does the cartridge hold the right key?' The combination is the real HRoT.
References
- Gassend et al., Silicon Physical Random Functions: Foundational PUF paper behind the silicon-variation and unclonability teaching model.
- Physical Unclonable Functions for Device Authentication and Secret Key Generation: PUF use for low-cost device authentication and volatile secret-key generation.
- RFC 5280: Internet X.509 Public Key Infrastructure Certificate and CRL Profile: Certificate profile background for the PKI and device-certificate portions of the lesson.
- NIST SP 800-57 Part 1 Rev. 5: Key-management reference for public/private keys and protection of cryptographic keys.
- NIST SP 800-193: Platform Firmware Resiliency Guidelines: General root-of-trust, protection, detection, and recovery vocabulary; not cartridge-specific.
- WithSecure, Printing Shellz: Printer and MFP security research context for why networked printers are security targets.
- HP Printer Security and Secure Cartridges: Official cartridge-security context: secure chips, tamper-resistant firmware, and printer-cartridge secure transactions.
- HP Anti-Counterfeit and Fraud Program: Official anti-counterfeit supplies context for genuine cartridge validation.
- PUFsecurity: PUF-based Security IP Solutions: PUF in semiconductor devices for chip identification, authentication, and unique device responses.
- Synopsys: Device-to-Host Authentication for Counterfeit Detection: PUF-based device-to-host authentication use case for counterfeit detection.
- Infineon OPTIGA TPM: Secure element, TPM, hardware root of trust, and protected credential-storage context.
Experiment: actual signatures, old state and anti-rollback
Verify an ECDSA response bound to the printer, cartridge and nonce, then read an AES-GCM protected counter. A response to an old challenge fails signature verification. An old counter can still have a valid tag; rejecting rollback needs a protected floor.
ECDSA, AES-GCM and random nonces are computed using classroom data. Each load creates a new trial, not persistent hardware state. Public-key trust, print permission and floor protection are supplied. It does not parse X.509, generate a physical PUF or prove OEM provenance, quality or lawful compatibility. A PUF or encryption alone does not create a monotonic counter.
Learning guide
How Trust Is Built Inside a Chip
Open the course outline → · Progress counts published lessons only
Prerequisites
- Public-key authentication and device identity
What I learned
- Model challenge-response authentication
- Explain break-one-break-all risk
- Connect PUF with secure state storage